CYBERWATCH-BD
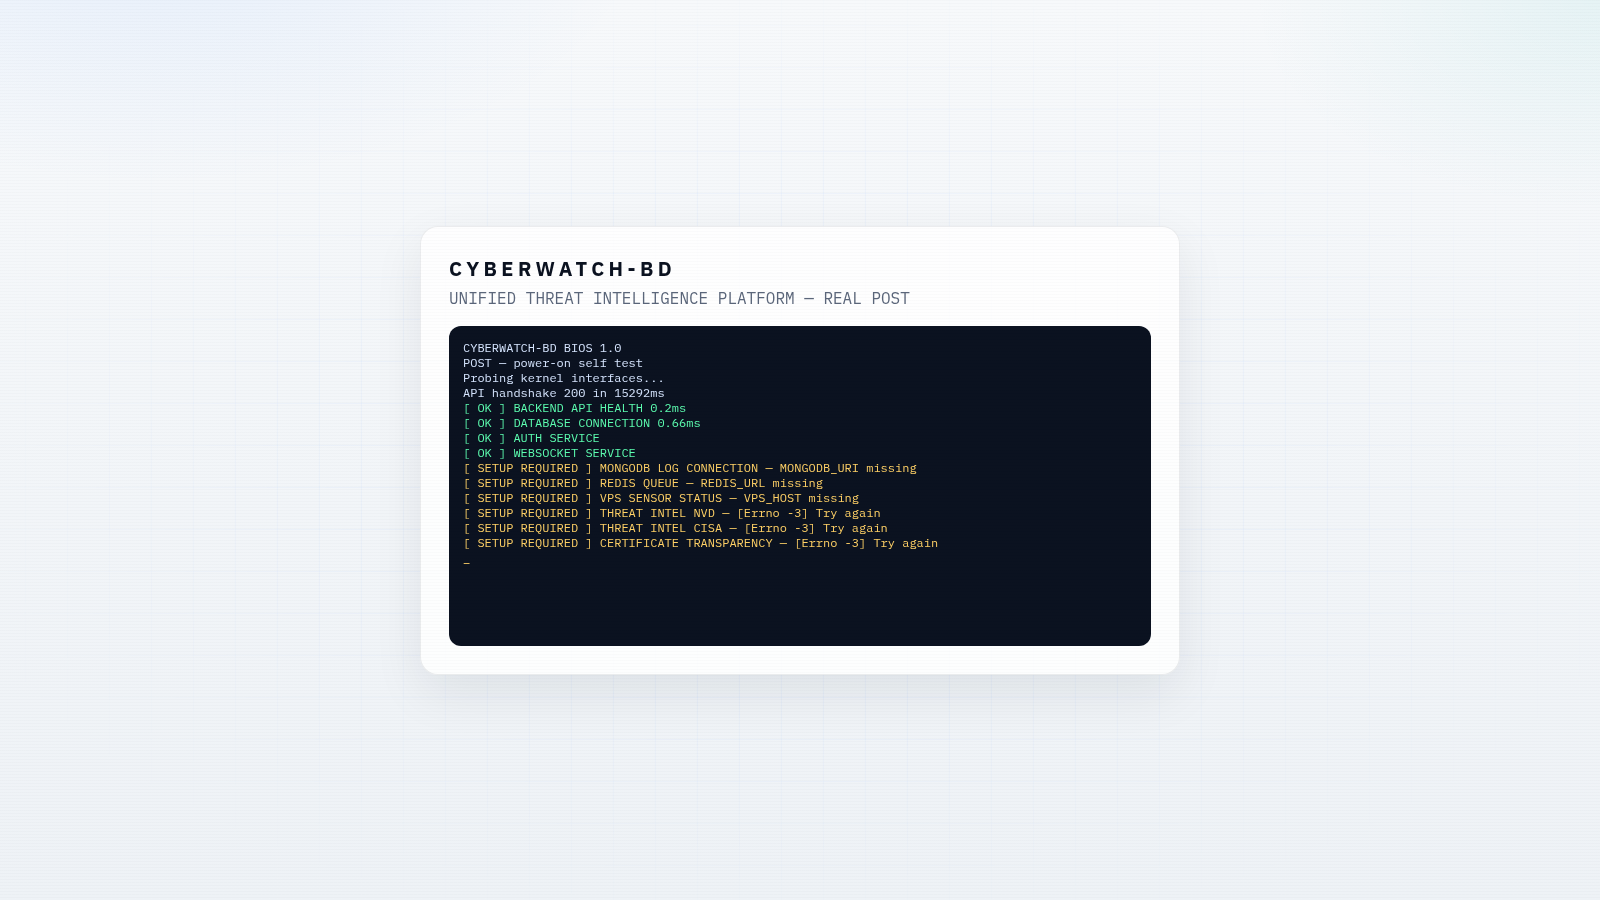
A unified browser SOC console for monitoring, triage and Bangladesh cyber defense
CYBERWATCH-BD is a security operations console that runs in the browser. It begins with a BIOS style power-on self test, then an authentication gate with pre-filled demo admin credentials. After signing in, a grouped sidebar exposes command, operations and mission modules: live host telemetry, AI alert triage, UEBA anomaly detection, automated response and approvals, offensive and defensive security operations, a predictive attack graph, threat intelligence and passive global intel, authorized scanning, incident management, real-time reports, a legal evidence desk, Bangladesh cyber watch tools, asset infrastructure, audit logs and settings. Most modules read live endpoints and render real computed results, while optional third party feeds remain clearly marked as setup required.
Highlights
Live host telemetry
Live CPU and memory
Local AI triage
AI alert scoring
Gated scanning
Grant-gated nmap
Bangladesh toolkit
Bengali fraud tools
Threat intel feeds
NVD, CISA, CRT feeds
How to Use
Sign in to the console
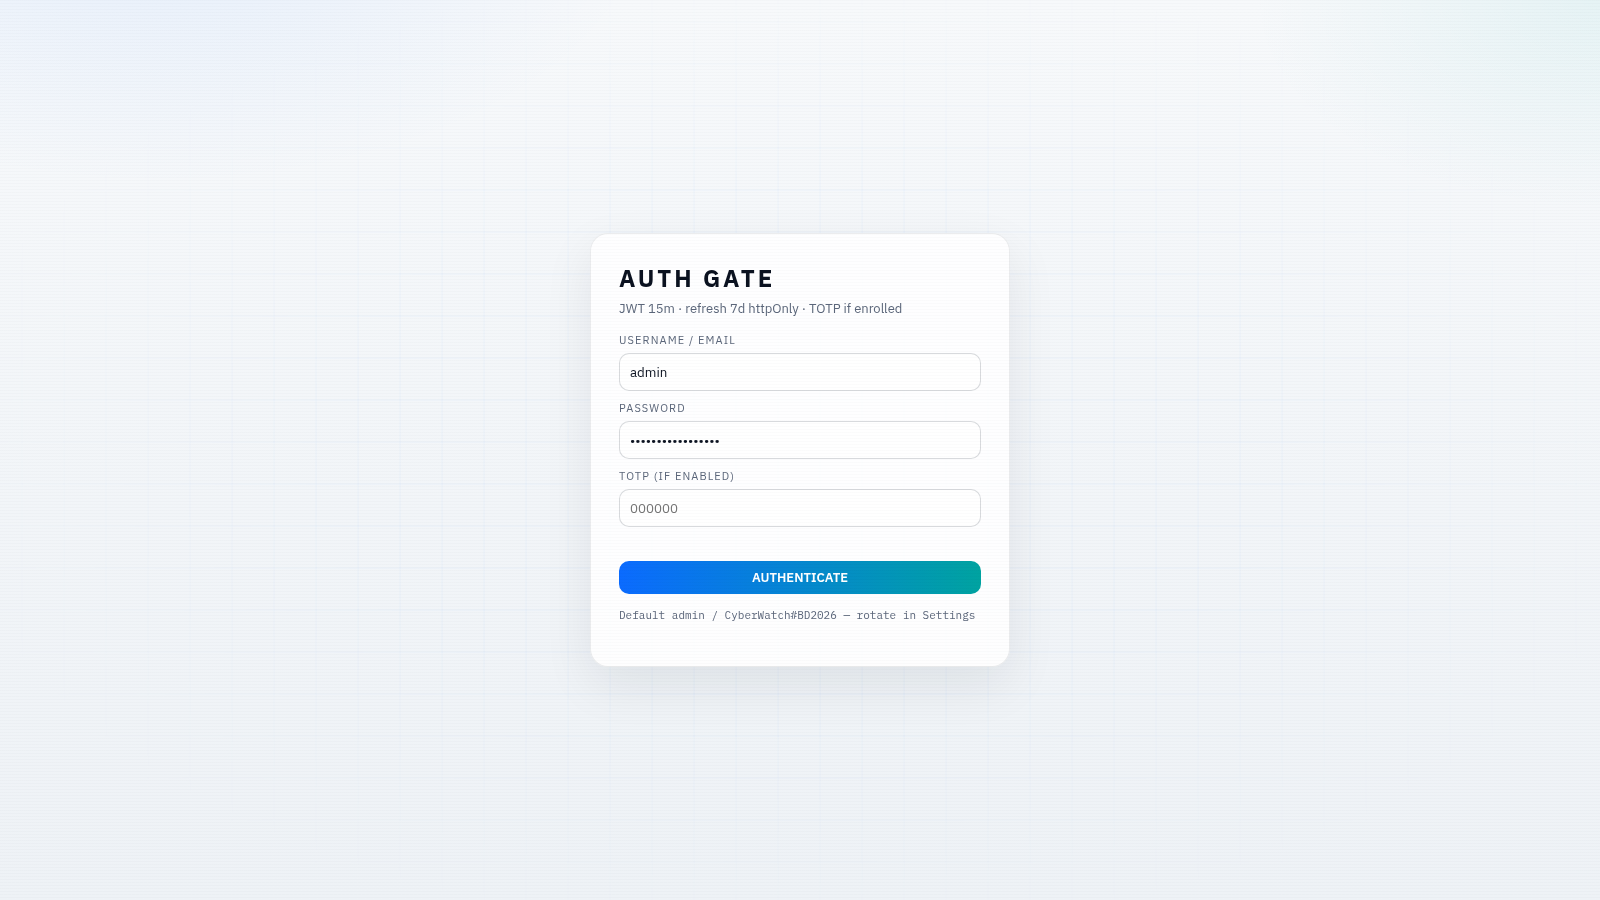
Open the site and let the boot sequence finish; it lands on an auth gate where the admin username and password are already filled in. Click AUTHENTICATE to reach the SOC Command Center. If TOTP is enrolled for the account, enter the six digit code before authenticating.
Read the command center
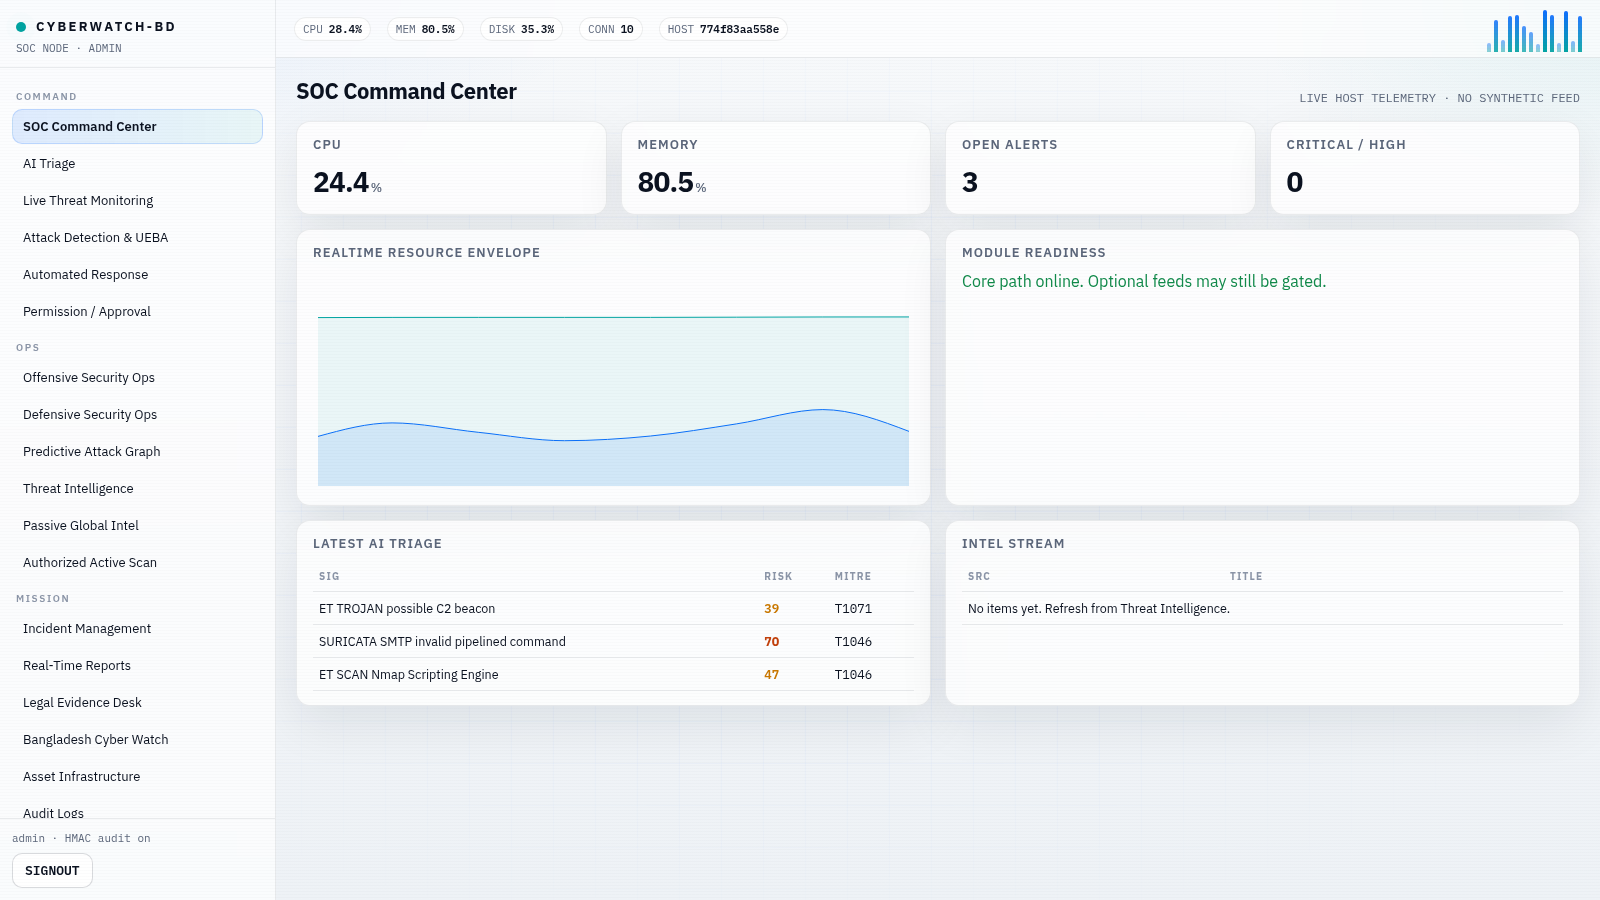
The dashboard shows live host telemetry for CPU, memory, disk, connections and host name, plus open alert counts, a realtime resource envelope chart and the latest AI triage rows. Use the grouped sidebar to move between COMMAND, OPS and MISSION pages; the telemetry strip stays visible on every page.
Work triage and monitoring
Open AI Triage to review the Suricata style event queue with timestamp, signature, risk and status columns. Live Threat Monitoring adds load averages, per core CPU, RX and TX counters and a top processes table. Attack Detection and UEBA accepts analyst behavior samples and scores them with a local Isolation Forest baseline.
Pull intel and run gated scans
On Threat Intelligence, refresh the public feeds such as NVD, CISA, CERT and certificate transparency; Shodan and HIBP stay optional until keys exist. Authorized scanning will not send packets until you create an authorization grant with a scope CIDR and document hash, then queue an nmap, zap or nuclei job against it.
Try the Bangladesh tools
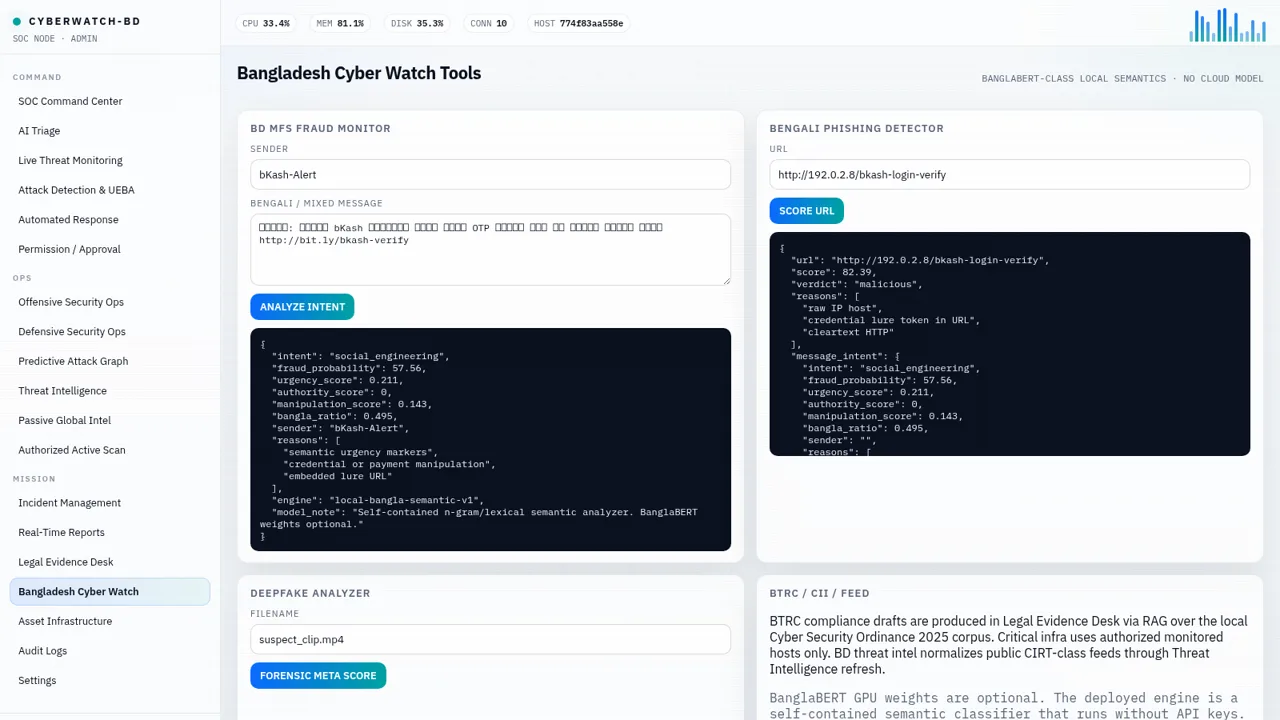
Bangladesh Cyber Watch provides a mobile financial services fraud monitor, a Bengali phishing URL scorer and a deepfake metadata analyzer, all running on a local semantic classifier without API keys. Legal Evidence Desk drafts compliance narratives from the bundled ordinance corpus; incident, report, asset and audit pages round out the workflow.
Similar Sites
 81
MonkeyCode AI Workspaces
AI coding workspaces for engineering teams
 45
ComposeLens
Visual Docker Compose inspector with graphs and security warnings
 24
9Router - AI Router
FREE AI coding router with auto-fallback, RTK token saving, 40+ providers
 23
Electric Code Assistant
Ultra-lightweight AI web IDE: build apps with AI, live preview, APK export
 14
CHOKESS AI
Browser-based AI coding agent with cloud workspace, terminal and live preview
 13
SiteAI — The AI Website Builder
The AI website builder that turns plain language into production-ready websites.